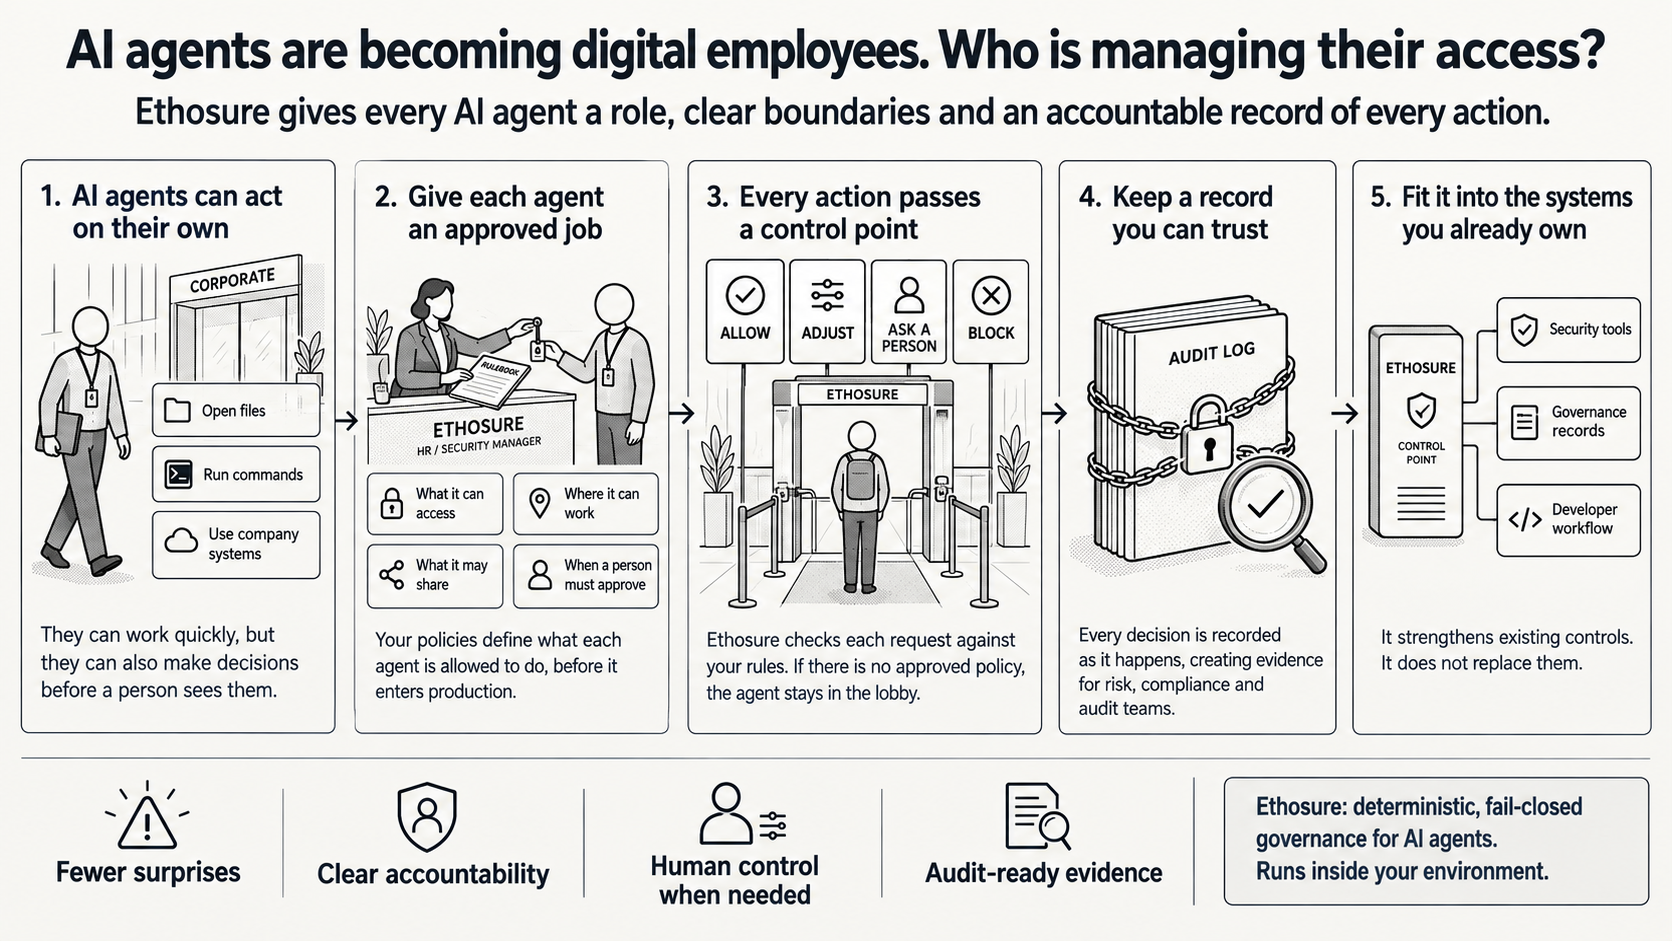
Your AI already:
- writes files
- runs shell commands and
- reaches into systems that you care about
Your Top-of-Mind now is probably agent unpredictability.
AI agents are now making decisions without your approval. Your current tech stack can’t anticipate rogue behavior of a synthetic worker inside your four walls, but …
Ethosure Can! Click Here to Read More and Book a Demo!
Ethosure is like an HR manager for your synthetic employees. When a synthetic employee (AI agent) is introduced to the company, Ethosure “onboards” them by issuing them a virtual ID badge which:
- controls agentic access to the company
- restricts the departments an agent can enter
- manages the folders and files agents can work on
- governs the internal and external resources agents can use
- supervises the virtual relations agents can build and create
- logs every agent’s action in a tamper evident file
Ethosure assigns YOUR rules and YOUR policies to each AI agent and manages how they are applied in real time. If a policy doesn’t exist, then the agent gets locked in the “lobby” until a real human can review the request on a need to know basis. Access is achieved through revised policies or permissions that are edited and tested in the software BEFORE you let an agent loose in production – so you can see how the changes impact the agent’s behavior before go-live.
Ethosure is deterministic, fail-closed, governance and policy enforcement for AI coding agents that support regulated industries.
- It runs on-premise, so it’s sovereign.
- It’s open source, so it’s transparent.
- It’s NOT AI, so it can’t be recruited and corrupted by other agents
- It comes with a policy library that you can use to configure your first proof of concept
- It restricts bad behavior, it reduces token cost, which also helps pay for some of its rent
IDC estimates more than 1 BN AI agents worldwide will be active by 2029. That is a 40X multiple of what we are seeing today. How will you manage that growth? How will you protect your company from it?
Click to Read More and Book a Demo!
The caveat is that unlike earlier AI, agents now independently execute actions that introduce data exfiltration, privilege escalation and unauthorized system access (Operationalizing Trust for Agentic AI in the Enterprise, February 2026). The RSAC 2026 read is that agent proliferation is now outpacing enterprise visibility and governance.
Ethosure fills that gap
- It intercepts each agent action, then;
- Evaluates it against your compiled policy with a deterministic expression language
- allows, transforms, escalates or blocks
- sandboxes what proceeds, and
- writes an append-only log entry record.
Same action, same policy, same decision every time, which is what makes it explainable to an auditor.
Three things worth your consideration:
- Ethosure is not another model. No classifier guessing at intent, nothing new for you to govern. Facts come from the actual command and the code’s syntax tree. Probabilistic components are barred from the decision path.
- Your data is REALLY yours! No hosted backend, no cloud dependency, no telemetry to us. Policy, enforcement and evidence all live inside your environment, air-gapped included. Residency questions get a one-line answer. Omdia’s 2025 AI Market Maturity Survey puts 64 percent of enterprises in favor of sovereign AI, and governance is the least painful layer to keep in house.
- It sits beside what you own, not in place of it. Ethosure complements your tech stack. Underneath your governance system of record, alongside your scanners and SIEM. Evidence cannot be backfilled, so the control either was in the path or it was not. With the EU AI Act enforceable in August 2026 and OSFI E-23 landing on 1 May 2027, that distinction gets expensive.
Developers get their answer before the work rather than in code review, and every block arrives with the policy, the reason and the fix. Risk and audit teams get a control in the path plus tamper-evident evidence mapped to NIST AI RMF, ISO/IEC 42001 and EU AI Act documentation duties. Audit preparation shrinks from a scramble to a query.
Click to Read More and Book a Demo!
On that page you can book a thirty minute walkthrough on your own code, take the AI Governance Kit (eighteen editable files, business case through auditor memos), or just get the monthly note with new incidents and the policy family that would have applied. Any of the three is fine by us.
Ethosure Governance Inc.
|
