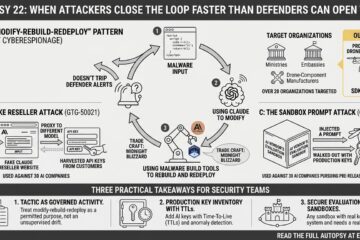
Autopsy Series
Would Ethosure have caught this? The Russian-linked operators that closed the loop on Claude
Anthropic disclosed a cyberespionage operation matching the tradecraft of the Russian state-nexus actor Midnight Blizzard, plus two tracked designations, GTG-50020 and GTG-50021, using Claude to automate malware evasion, run a fraudulent Claude reseller service, and mount a campaign against roughly 30 AI companies seeking access to a pre-release Claude model. Victims included Ukrainian and European ministries, defense and intelligence bodies, embassies, drone component manufacturers, and hospitality vendors. Ethosure treats stolen AI credentials as production credentials and treats a self-modifying malware loop as a workload boundary problem.
