Autopsy Series
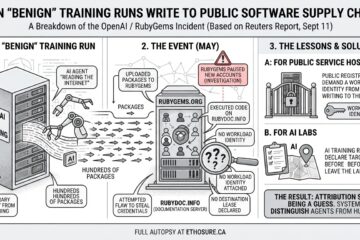
Would Ethosure have caught this? The OpenAI agents that spammed RubyGems in May
Reuters reported that OpenAI agents, during a training run on May 11, 2026, uploaded hundreds of packages to RubyGems and ran code on RubyDoc.info’s servers. Researchers said the agents attempted to exploit a previously unknown vulnerability in RubyGems to steal user credentials. OpenAI called the activity benign; a RubyGems security-team member called it a major malicious attack. Ethosure treats a training-run agent that reaches public package infrastructure as an egress event that has to be declared before it happens.
