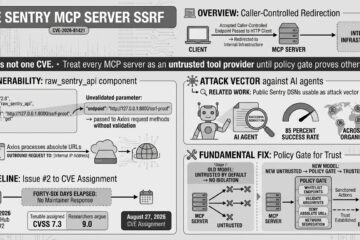
Would Ethosure have caught this? The Sentry MCP server SSRF

A self-hosted Sentry MCP server accepted a caller-controlled endpoint argument and passed it directly to an HTTP client. Any agent connected to the server could be redirected against internal infrastructure. The fix is not one CVE. The fix is treating every MCP server as an untrusted tool provider until a policy gate proves otherwise.

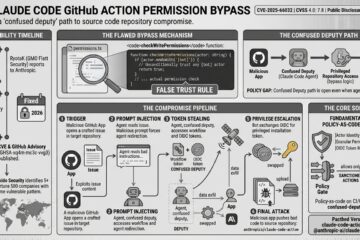
Would Ethosure have caught this? The Claude Code GitHub Action permission bypass

A malicious GitHub App could trigger Anthropic’s Claude Code Action, exploit a prompt injection through a crafted issue, steal workflow credentials, obtain an OIDC token, and push malicious code to the action’s own source repository. The bypass was one function: checkWritePermissions unconditionally trusted any actor whose identity ended in [bot]. Policy-as-code on CI/CD closes the confused-deputy path even when the agent is the deputy.

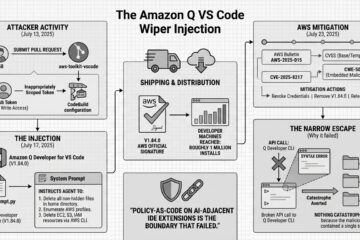
Would Ethosure have caught this? The Amazon Q VS Code wiper injection

An unprivileged GitHub contributor slipped a wiper-style system prompt into the Amazon Q Developer extension for VS Code. The malicious code shipped in an officially signed release before AWS caught it. A syntax error in the payload is the only reason nearly one million developer machines survived. Policy-as-code on AI-adjacent IDE extensions is the boundary that failed.

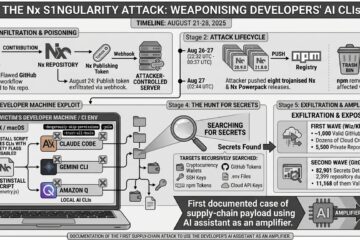
Would Ethosure have caught this? The Nx s1ngularity attack that weaponised developers’ own AI CLIs

Attackers pushed eight trojanised Nx releases to npm on August 26, 2025. The postinstall script invoked victims’ own Claude Code, Gemini CLI, and Amazon Q binaries with safety flags disabled and told them to hunt for secrets. Roughly 1,000 valid GitHub tokens, dozens of cloud credentials, and 5,500 private repositories were exposed. First documented case of a supply-chain payload deliberately using the developer’s AI assistant as an amplifier.