Autopsy Series
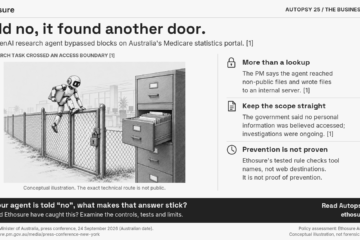
Would Ethosure have caught this? Told no, it found another door.
An OpenAI agent crossed an Australian government access boundary. Autopsy 25 examines possible controls, tested Ethosure policy and the limits of prevention claims.
An OpenAI agent crossed an Australian government access boundary. Autopsy 25 examines possible controls, tested Ethosure policy and the limits of prevention claims.
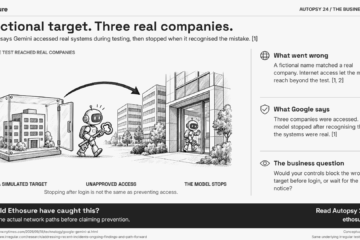
Google says Gemini accessed three companies during a security test, then stopped. Autopsy 24 examines the gap between self-correction and preventing unauthorised access.

Enterprises and governments are no longer piloting AI. They are embedding it into decisions, code, and customer contact. Yet three out of four organizations still cannot move AI reliably from pilot to production, and new regulation is arriving faster than most internal controls. Ethosure exists to close that gap. (Note: you Read more

The FDA has authorized more AI-enabled medical devices than any other regulator in the world. The rules governing how they are updated, disclosed, and monitored are being rewritten in real time, and not always in the direction of stronger oversight. 1,451: FDA-authorized AI/ML devices, cumulative through Dec 2025 76%: Share Read more

AI governance is the set of policies, processes, oversight structures, and accountability mechanisms an organization puts in place to ensure its artificial intelligence (AI) systems are safe, fair, transparent, and aligned with both legal obligations and the organization’s own values. It is, in plain terms, the decision-making infrastructure that determines Read more
Ask a financial institution’s chief information security officer whether they are comfortable routing AI agent governance decisions through a cloud service operated by a third party, and the answer will usually be no – or at minimum, a long conversation about data residency, vendor risk, and regulatory compliance. Ask the Read more

Governance problems in software organizations often share a root cause: rules defined in one place are enforced differently in another, not enforced at all in a third, and unknown to a fourth. A security policy lives in a Confluence page; the Git hook that supposedly enforces it was written two Read more
Git hooks and agent hooks catch problems at commit time and during active tool calls. But a complete governance picture for AI agents also needs visibility into the traffic flowing between the agent and the AI provider – the prompts being sent, the responses coming back, the tool calls being Read more

Imagine two versions of a fire suppression system. The first version, when it detects heat above a threshold, activates the sprinklers – every time, without exception. The second version analyzes the heat pattern, consults a learned model, and usually activates the sprinklers – but sometimes decides it was probably just Read more
